01
Security Strategy & Architecture
Translate business risk into a security roadmap, target architecture, and priorities teams can act on.
Techhands helps organizations reduce exposure, strengthen resilience, and respond with confidence by connecting strategy, identity, endpoints, cloud, networks, and security operations.
Strategy, identity, protection, detection, and response—connected from the start.
Cybersecurity works when identity, endpoints, cloud, networks, data, and response operate as one system. Techhands brings those layers together through CentrSec™—a practical security model built around visibility, control, and continuous improvement.
Translate business risk into a security roadmap, target architecture, and priorities teams can act on.
Protect access with modern identity, MFA, conditional controls, privilege management, and zero-trust principles.
Secure endpoints, email, cloud, and networks with layered controls, continuous monitoring, and actionable visibility.
Prepare response roles, containment decisions, recovery dependencies, and exercises before an incident occurs.
Techhands helps you operate and innovate at enterprise speed with resilient, security-first architectures. We design environments that help prevent breaches, reduce the impact of incidents, withstand failures, and recover quickly, while providing the visibility, evidence, and assurance required by regulators, leadership teams, and boards.
Techhands’ Cyber Advisory service provides outcome-focused guidance to define and strengthen your security strategy, Zero Trust roadmap, and cyber resilience across identity, networks, cloud, data, and operations. Every recommendation is tailored to your organisation’s specific risk profile, priorities, and business goals.
Techhands goes beyond implementing individual security tools. Our technical experts help secure platforms across networks, data centres, cloud, data, AI, and hybrid environments, turning insights from each control into a stronger, more coordinated security posture across your entire technology estate.
Techhands Managed Security Services combine 24×7 monitoring, detection, and response with CentrAI™ to support your team. We integrate managed SOC, XDR, exposure management, and cyber recovery to reduce risk, strengthen resilience, and free your team for more strategic security initiatives.
Techhands helps organisations reduce cyber risk by applying AI-driven monitoring, analytics, and automation across their IT environment. Our specialists identify emerging threats, prioritise vulnerabilities, and accelerate response actions—giving security teams clearer insight, faster decision-making, and stronger protection against evolving cyber threats.
Techhands works across identity, endpoints, email, cloud, networks, and day-to-day operations. We strengthen what already exists, close the gaps that matter, and remain accountable for how protection performs over time.
Tools matter. The way identity, prevention, detection, and response work together matters more.
Perspectives for leaders balancing risk, resilience, and the pace of change.
Why asset visibility, ownership, and business context should come before another security tool is added.
Read insight →
A practical framework for strengthening access without creating unnecessary friction for users or administrators.
Read guide →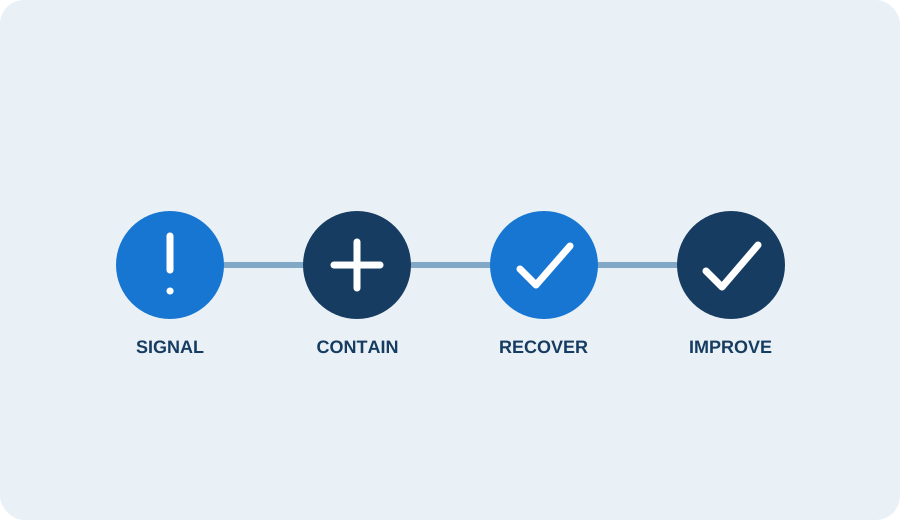
How clear roles, rehearsed decisions, and dependable recovery reduce the cost of uncertainty during an attack.
Read insight →Clear expectations make security decisions faster, ownership stronger, and response more dependable.
We align the scope to your environment and risk priorities. Engagements can include security assessment, architecture, identity, endpoint and email protection, cloud and network controls, monitoring, incident readiness, and ongoing security operations.
Yes. We begin by understanding the controls already in place, how they are configured, who owns them, and where coverage or operational gaps remain. We improve and integrate useful investments before recommending unnecessary replacement.
CentrSec™ is Techhands’ coordinated security approach. It brings identity, endpoint, email, network, cloud, policy, monitoring, and response into one operating model so security can be managed and measured as a connected system.
Monitoring and response are scoped in the service agreement. We define coverage hours, monitored systems, who investigates, who can authorize containment, and any partner-delivered services before onboarding.
We document roles, escalation, communications, containment authority, and recovery dependencies, then exercise the plan. This is planned incident readiness; the general inquiry form is not an emergency response channel.
Tell us what needs to improve, what must keep working, and the decision you need help making.
Start a Conversation →A focused conversation to understand the need and agree whether there is a useful next step.
The problem, its business impact, and what a useful result would look like.
The systems, people, providers, and constraints already in place.
Whether discovery, advice, a project, or operational support fits the need.