Cybersecurity starts with operational truth.
Why asset visibility, ownership, and business context should come before another security tool is added.
A control cannot protect an unknown service
Security discussions often begin with products. Yet the most basic questions can remain unanswered: Which devices and applications exist? Who owns them? What information do they hold? Which business activity stops if they fail?
Across professional services, retail, healthcare, and manufacturing, incomplete answers make it difficult to judge whether current controls cover the actual environment.
Reconcile the operational picture
Techhands starts with the available evidence: device inventories, cloud accounts, application lists, identity records, and support information. Differences between those sources are useful findings, not administrative noise.
An unmanaged device, an unused privileged account, or an application without an owner needs investigation. The objective is a working inventory that can inform decisions, with a process for keeping it current.
Illustrative finding-to-action record
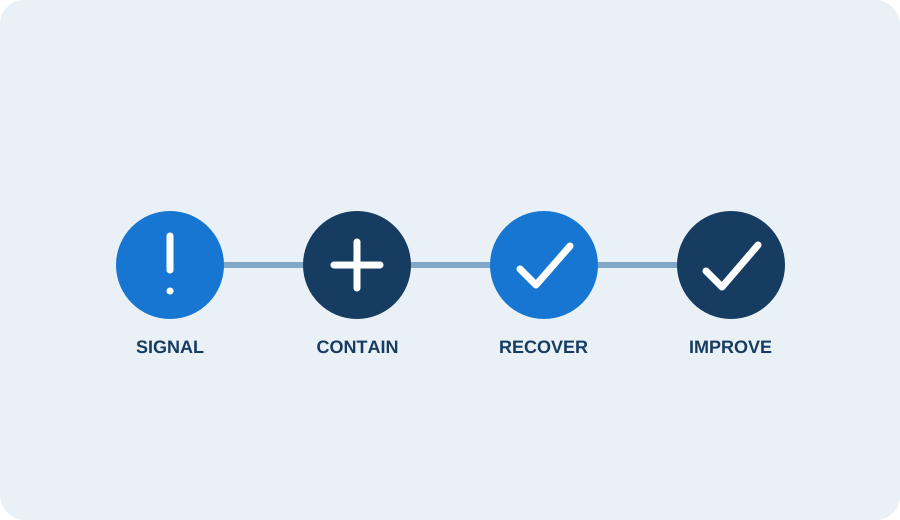
Example: an asset appears in the device inventory but has no matching endpoint-protection record. First verify whether this is a naming mismatch, a retired device, or an active coverage gap. Assign an owner and record the device's business purpose, exposure, and current controls. The owner agrees remediation or a documented exception, a due date, and the evidence required to close the action. A matching inventory entry alone is not proof that the protection is functioning.
Prioritize with business context
Vulnerability and security tools produce technical findings. Service mapping adds context about exposure, dependencies, data sensitivity, and operational impact. Together, they help teams decide what to address first.
This does not mean ignoring a severe finding because its owner is unclear. It means making ownership and uncertainty part of the response rather than allowing a report to move between teams indefinitely.
Build a stronger basis for the next investment
The outcome is a clearer view of what is covered, what is missing, and who must act. A proposed new tool can then be assessed against an identified gap.
Security improves through sustained ownership of those basics. A smaller set of well-operated controls can be more useful than a larger collection whose coverage nobody can explain.